Hi,
I’m currently running XWiki 18.7.0.
I remember moving away from the distribution-provided Tomcat packages because the Linux distribution’s support policy and XWiki’s support matrix no longer aligned well. I don’t recall the exact reasons, but I believe security considerations played an important role. If I remember correctly, I needed to migrate to Tomcat 10, which was not readily available through the distribution packages at the time.
The current software stack is composed of:
rjr@e220i057h096l:~$ cat /etc/lsb-release
DISTRIB_ID=Ubuntu
DISTRIB_RELEASE=22.04
DISTRIB_CODENAME=jammy
DISTRIB_DESCRIPTION="Ubuntu 22.04.5 LTS"
rjr@e220i057h096l:~$ sudo /opt/tomcat/bin/version.sh
Using CATALINA_BASE:   /opt/tomcat
Using CATALINA_HOME:   /opt/tomcat
Using CATALINA_TMPDIR: /opt/tomcat/temp
Using JRE_HOME:        /usr
Using CLASSPATH:       /opt/tomcat/bin/bootstrap.jar:/opt/tomcat/bin/tomcat-juli.jar
Using CATALINA_OPTS:
Server version: Apache Tomcat/10.1.60
Server built:   Sep 9 2026 22:35:59 UTC
Server number:  10.1.60.0
OS Name:        Linux
OS Version:     6.8.0-138-generic
Architecture:   amd64
JVM Version:    21.0.12.1+1-1-22.04.4-Ubuntu
JVM Vendor:     Ubuntu
APR loaded:     false

Third-party libraries:
  jakartaee-migration-1.0.12-shaded.jar: 1.0.12
  ecj-4.27.jar:                          3.33.0.v20230218-1114
rjr@e220i057h096l:~$ mysql -u xwiki -p -N -B -e "SELECT VERSION();"
Enter password:
8.0.46-0ubuntu0.22.04.4
rjr@e220i057h096l:~$
I’m preparing an update to 18.8.0, but before I would lilke to eliminate or at least understand all security vulnerabilities warnings offered by the Security Vulnerabilities extension. I understand that it is currently experimental.
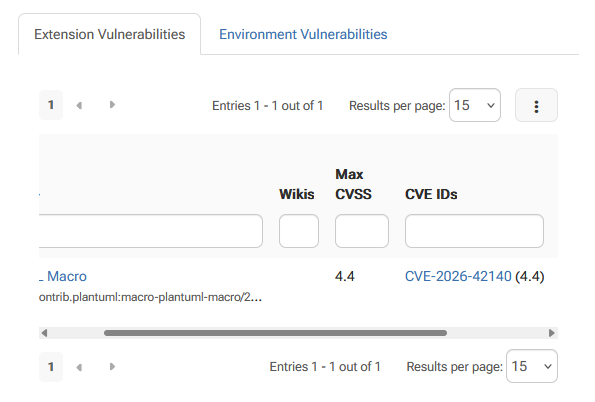
The list in the Extension Vulnerabilities tab contains only one entry:
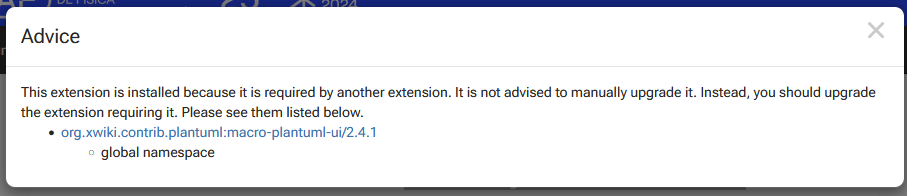
The advice reads:
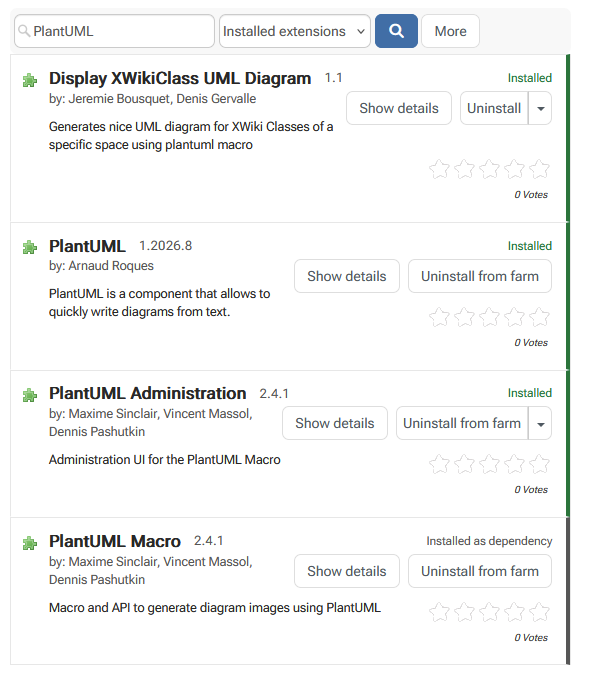
And I think this is the release of the PlantUML extension that we have installed:
PlantUML is working great here, but using local and remote rendering.
Please, do you understand why we are still getting the warning about that security vulnerability in PlantUML macro?
Thanks!